InfoSecBulletin Cybersecurity for mankind
AnyDesk, a German remote access software company, has confirmed that their production systems were compromised in a security incident. They have 170,000 customers worldwide, including Comcast and Thales.
The company’s client logins were not working for three days. During this time, the company informed the customers about unexpected maintenance. According to the changelog, the company cancelled a code signing certificate on January 29th.That suggests its previous code signing certificate was compromised.
Daily Cyber security update for 14.11. 2026

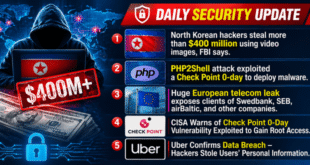
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

Now on Friday, February 2, AnyDesk reported: “Following indications of an incident on some of our systems we conducted a security audit and found evidence of compromised production systems. We immediately activated a remediation and response plan involving cyber security experts CrowdStrike…”
AnyDesk hacked: No ransomware, no details:
The incident wasn’t caused by ransomware, according to AnyDesk, a company established in 2014 with customers in 190 countries. They also stated that they have no evidence of end-user devices being affected.
“We can confirm that the situation is under control and it is safe to use AnyDesk. Please ensure that you are using the latest version, with the new code signing certificate” it added, in a distinctly detail-thin report.
Code-signing certificates, provided by a trusted third party like a certificate authority, contain software information. When the software is installed, the Operating System verifies the signature using the certificate to ensure it has not been altered. If the signature is invalid, it can be used to sign malware, making systems believe it is from a reliable source.
The company did not clearly say that its certificate was stolen. However, a security researcher named Florian Roth quickly made a YARA rule to find binaries that were signed with a possibly compromised certificate from AnyDesk. He found over 2300+ binaries signed with that certificate.
AnyDesk said: “We have revoked all security-related certificates and systems have been remediated or replaced where necessary. We will be revoking the previous code signing certificate for our binaries shortly…
“Our systems are designed not to store private keys, security tokens or passwords that could be exploited to connect to end user devices.
“As a precaution, we are revoking all passwords to our web portal, my.anydesk.com, and we recommend that users change their passwords if the same credentials are used elsewhere,” it added in its update.
AnyDesk did not provide any additional details or Indicators of Compromise and released the advisory at 11pm German time.
Security professional Jake Williams noted on X: “This is a strategic move considering they had taken systems offline several days ago. Transparent companies do not engage in such tactics.
He added: “Threat hunt in your environment anywhere you had AnyDesk installed for anomalous activity over at least the last 30 days. When the intrusion vector isn’t being shared, you have to presume they don’t yet know. Even if they know, it’s usually a leap to say what was accessed. Think about it: do you think a threat actor jumped onto one machine and pulled a code signing cert and that’s it? No? Oh, okay. Consider disabling AnyDesk in your environment, either by disabling the agent through GPO or blocking at a network level until more is known. I don’t have any inside knowledge on this particular incident. But I’ve worked plenty of incidents in my day and the reporting on this one stinks to high heaven.”