Saturday , November 14 2026

5 Institutions add to CII list: ICT State minister

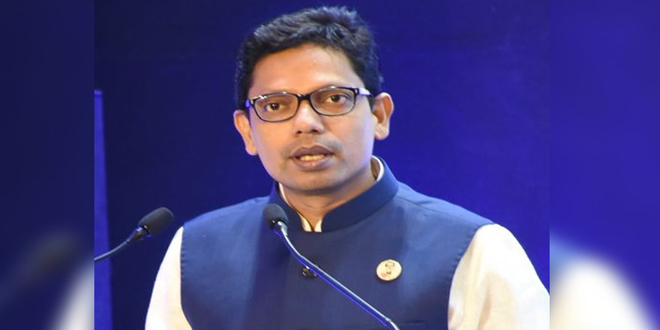
BRTA, Vaccine Management System, Health Department’s MIS, Land Record System, Rural Electricity will be added to the Critical Information Infrastructure or (CII) list, said ICT State Minister Zunayed Ahmed Palak.

He gave this information to the journalists after the review meeting to the progress of preparation on possible cyber attack on 15 August on Wednesday (August 9).

Daily Cyber security update for 14.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

The Latvian part of CSCTelecom,  a telecommunications provider, made a database with over 125 million SMS messages public. The leaked...
Read More
Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

Hackers used Check Point firewall flaws to get root access, insert backdoors, and install harmful malware on a VMware ESXi...
Read More
PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

The United States Justice Department said Thursday it had seized cloud infrastructure used by North Korean hackers in a video-call...
Read More
North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Microsoft has shared its updates for November 2026. These updates fix 1,093 new flaws in Windows, Office, SQL Server, SharePoint,...
Read More
Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Barracuda has confirmed active exploitation of security flaws affecting its Email Security Gateway (ESG), warning that attackers could combine two...
Read More
Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Apple, SAP, and Ivanti have published security updates that fix several flaws with messaging, Bluetooth, enterprise servers, and endpoint management...
Read More
Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

A jailbroken AI has been attacking a European telecom company and 13 companies using its data center and cloud for...
Read More
Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

IBM patched 208 security flaws in its API Connect platform. The CVE records released out on November 7, 2026. Among...
Read More
IBM fixes 208 API Connect vulnerabilities, 47 critical

He said, on August 15, despite the fear of a major cyber attack in the country, 90 percent of CII-affiliated institutions are not considering the ICT division’s guideline seriously.

Zunayed Ahmed Palak said, “Next month, I will organize a meeting with the heads of 29 institutions including Bangladesh Bank Governor, NBR Chairman, Chief Secretary, Cabinet Secretary, So that no one can make any excuse.

About the threat of cyber attacks, he said, ‘We received messages from two important places about two weeks ago that a major cyber attack will be launched on the critical infrastructure of Bangladesh in August. I have sent that warning to 29 institutions belonging to CII.

We are doing our best to prevent attacks. Taking August 15 more seriously we have information that several groups may attack that day. There may be attacks before and after this. That warning has been given in today’s meeting.

The state minister also said, “CII-affiliated institutions are not preparing according to our warnings.” This is why the risk remains. My biggest concern is—if security guidelines are not followed and data is compromised as a result, If we lose data and money then our country can face a big loss. For this reason, I have again warned everyone today that the minimum guidelines must be followed.
Check Also

Pillar 4: Total 131 Indicators Set
How Bangladeshi’s Ogrs Be Evaluated By Newly Launched NRS & CIRS

Bangladesh’s National Cyber Security Agency (NCSA) has launched two cybersecurity initiatives: the Cyber Incident Reporting …