 InfoSecBulletin Cybersecurity for mankind
Security researchers found at least 120 Cisco Secure Email Gateway and Cisco Secure Email and Web Manager devices vulnerable to a critical zero-day flaw that is being actively exploited.
CVE-2025-20393 is a vulnerability with no patch available, putting organizations at risk. Threat intelligence from Shadowserver Foundation indicates that vulnerable devices are part of over 650 exposed Cisco email security appliances available online.
Japan banking crisis
Outage causes disruption at 128 japan banks: preventing ATM transaction

Daily Cyber security update for 06.11. 2026

Cyber attack causes French bank Credit Mutuel Arkea €100 million missing

OpenAI AI Pipeline Discovers 948 Linux Kernel Privilege Escalation Flaws in 30 Hours

Bangladeshi Researcher Rasel Earns First Apple CVE Recognition for Model I/O Flaw

WinRAR, WordPress RCE flaw & Zyxel GS1900 Zero-Day exploited in the wild

Daily Cyber security update for 04.11. 2026

Daily Cyber security update for 03.11. 2026

Using ARTEX AI, Hacker to attack 200 Organizations Across 14 Countries

Amadeus cyber incident impacted “Cathay Pacific, Qantas, Japan, Malaysia, Korean & Asiana” Airlines

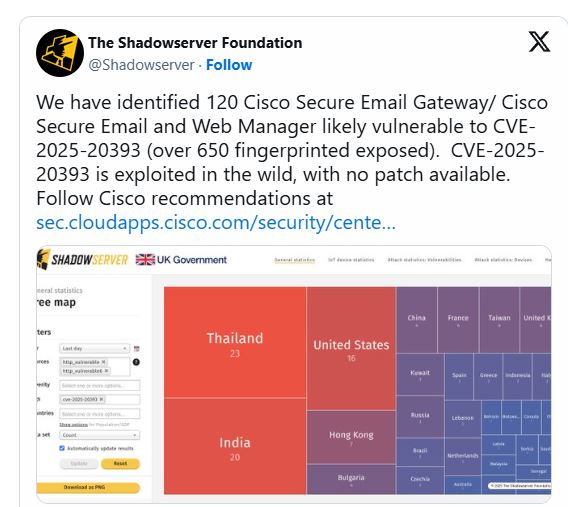
The discovery raises major concerns for organizations that depend on these systems to filter harmful emails and protect against phishing and malware.
Cisco has acknowledged the vulnerability and released a security advisory urging organizations to implement immediate defensive measures.
The networking company advises affected clients to check their security settings and implement temporary fixes until a permanent solution is ready. Organizations can find detailed guidance on Cisco’s Security Advisory portal.
Organizations continue to struggle with zero-day vulnerabilities, especially in vital components like email gateways. Security teams using Cisco Secure Email Gateway and Web Manager should quickly review the advisory and implement the recommended countermeasures.
In the mean time, a simple Python script to help organizations quickly detect exposure to CVE-2025-20393, a critical zero-day vulnerability in Cisco Secure Email Gateway (SEG) and Secure Malware Analytics (SMA).
The “Cisco SMA Exposure Check” tool identifies open ports and services exploited in recent attacks, as noted in Cisco’s advisory.
GitHub user StasonJatham released a script today that identifies indicators of compromise related to a vulnerability. This flaw lets unauthorized remote attackers run arbitrary code through exposed management and quarantine interfaces.
The tool scans and identifies HTTP/S signatures by examining server headers, status codes, redirects, authentication realms, Cisco keywords, and version patterns. It also checks common paths like /quarantine, /spamquarantine, /spam, /sma-login, and /login.
It also grabs raw socket banners and flags indicators of active exploitation, including strings like “AquaShell,” “AquaTunnel,” “Chisel,” and “AquaPurge” – hallmarks of post-compromise tools observed in the wild.
Tool Unveil to Detect Cisco Secure Email Gateway 0-Day Vulnerability



