Tuesday , October 27 2026
SafePay

SOCRadar Report
Emerging “SafePay” Ransomware Infected 260+ Victims Worldwide

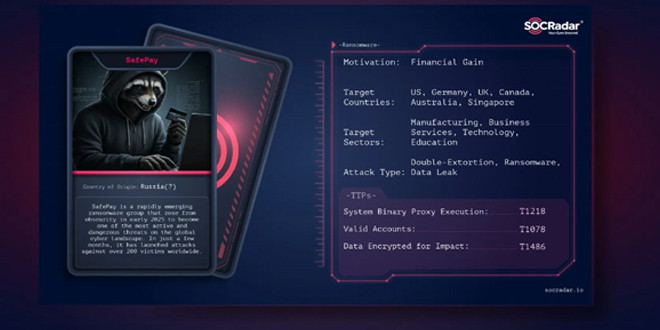
A new ransomware threat in 2025, SafePay, has executed over 265 attacks across various continents. The group emerged in September 2024, initially targeting around 20 victims. Since early 2025, it has significantly intensified its operations and now poses a serious threat in global ransomware.
Source: SOCRadar

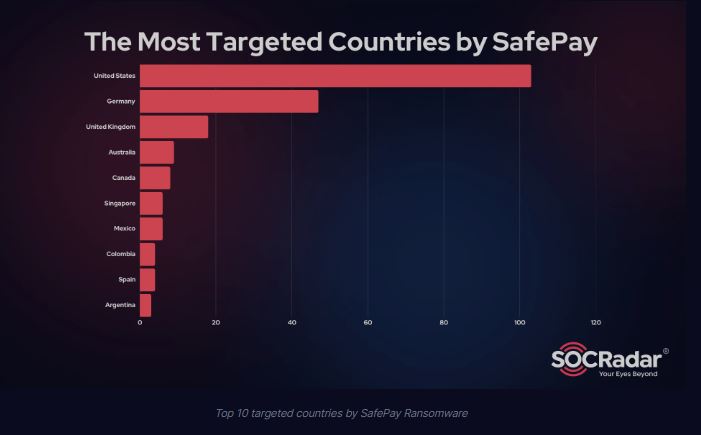
SafePay’s victims are mostly in developed economies, showing a targeted strategy. The United States has 103 confirmed victims, nearly 40% of all cases, followed by Germany with 47 recorded incidents.

CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

CISA has updated a new alert to reflect the addition of CVE-2026-109618 and CVE-2026-109619 to its Known Exploited Vulnerabilities (KEV)...
Read More
CISA adds PHP2Shell to KEV, PHP Releases New Security Updates to Fix Critical HTTP2Shell flaw

Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Cloudflare has shared an urgent update to its Web Application Firewall (WAF) rules due to CVE-2026-111497, a Brotli issue. The release...
Read More
Cloudflare Unveils Emergency WAF Ruleset Update on Brotli flaw

Daily Cyber security update for 26.10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 26.10. 2026

The Washington Post report
Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

AI startup Cathedral gained a limited access to internal systems at Anthropic in less than 12 hours, exposing employee information,...
Read More
The Washington Post report  Ex-DOGE AI startup Cathedral Breaches Anthropic Internal Systems within 12 Hours

Daily Cyber security update for 25. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 25. 10. 2026

Daily Cyber security update for 24. 10. 2026

Cyberattacks are rising around the world, including ransomware, malware, data leaks, and hacked websites. These events show how complex and...
Read More
Daily Cyber security update for 24. 10. 2026

PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

The PHP security team shared ways to protect against a new flaw that lets someone run unwanted code on certain...
Read More
PHP shares new RCE flaw (CVE 2026-115560) with no patch but mitigation

US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Major US banks have detected unauthorized access to customer accounts by third-party AI agents, with some systems taking actions beyond...
Read More
US banks faced unauthorized access by AI agents in customer accounts: Axios reports

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated...
Read More
Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

Hacker offers to sell Rajasthan Government’s Department of Information Technology & Communication (DoIT&C) data in a underground forum. The threat...
Read More
Hacker claim to access Rajasthan Police data: 70,000 records allegedly exposed

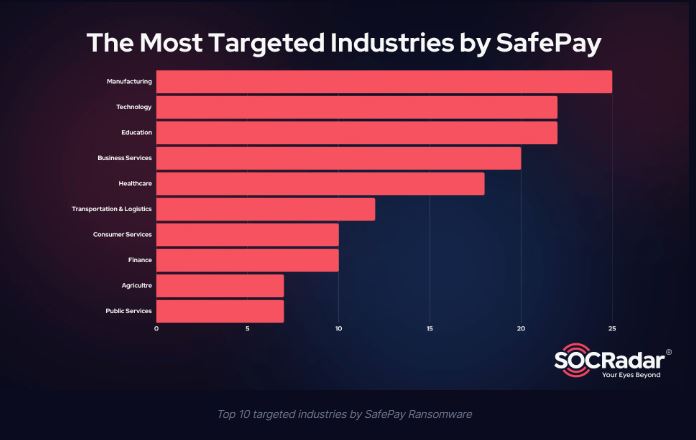
Targets also include the United Kingdom, Australia, Canada, and several countries in Latin America and the Asia-Pacific. SOCRadar analysts found that SafePay intentionally avoids targeting organizations in Commonwealth of Independent States countries using a language detection feature.
Source: SOCRadar

The malware has checks that immediately stop it from running if the system uses Armenian, Azerbaijani, Belarusian, Georgian, Kazakh, Russian, or Ukrainian languages, indicating that the operators want to evade legal action in these areas.

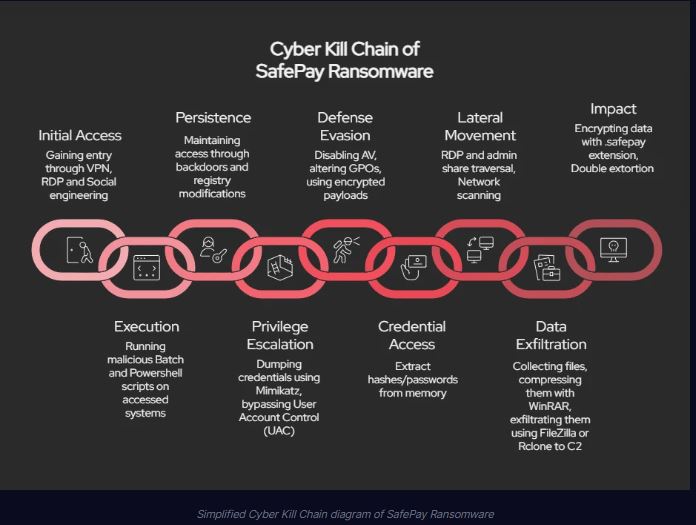
SafePay operators routinely disable Microsoft Defender and other security measures using administrative commands and Group Policy changes, including adding folder exclusions and turning off real-time protection.
Source: SOCRadar

The malware uses encrypted strings, dynamic loading, and advanced packing techniques to avoid detection. Click here to read the full report.

ChatGPT, Top 5 GenAI Tools Vulnerable to Man-in-the-Prompt Attack

Check Also

Fortinet

Atlassian patched 176 flaw in Jira and Confluence: Fortinet Urges to Patch Flaws Affecting FortiOS, FortiManager

Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for …