 InfoSecBulletin Cybersecurity for mankind
GitHub said that about 3,800 internal repositories were hacked because of installing a harmful VS code extension by an employee.
Claude AI Cracks 25-Year NSA Cryptography Number Mystery in Just 30 Minutes

Bypassing firewalls, AI Agents Accessed Indian ‘ Data Without Permission: CERT-In

MITRE ATT&CK v20 Unveils 9 New Attack Techniques On AI Exploits, MFA Bypass, and CAPTCHA Evasion

Hackers Exploit Fortinet Flaws to Deploy Stealthy PEERSTITCH Malware on FortiGate Firewalls

Hacker stole Meta GitHub repos; Stole Source Code

Urgent patch! Zoom,NVIDIA and IBM Patch 41 Security flaws

Microsoft patches record braking 1411 flaws; 2 zero days

Anthropic unveils “OSS Scanner” Free AI Vulnerability Scanner for Open-Source Projects

Rise on RCE Exploits Targeting Hikvision Camera Flaw

FortiBleed Attack Compromised 80,000+ Devices, SonicWall Patches 4 SMA1000 Flaws CVSS 10
“Yesterday we detected and contained a compromise of an employee device involving a poisoned VS Code extension. We removed the malicious extension version, isolated the endpoint, and began incident response immediately,” the company said.
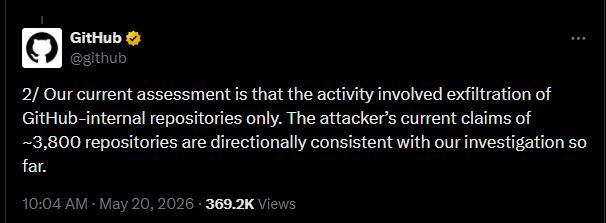
“Our current assessment is that the activity involved exfiltration of GitHub-internal repositories only. The attacker’s current claims of ~3,800 repositories are directionally consistent with our investigation so far.”
The TeamPCP hacker group said they accessed GitHub’s source code and claimed they have almost 4,000 private repositories. They are asking for at least $50,000 for the stolen data.
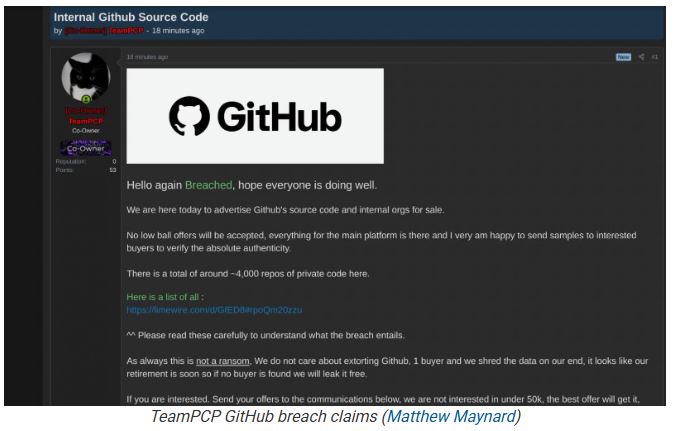
“As always this is not a ransom, We do not care about extorting Github, 1 buyer and we shred the data on our end, it looks like our retirement is soon so if no buyer is found we will leak it free,” the cybercriminals said. “If you are interested. Send your offers to the communications below, we are not interested in under 50k, the best offer will get it.”
GitHub quickly removed the harmful extension version, cut off the affected device, and started its response plan.
GitHub found that the attacker took data from internal repositories only. There is no proof that public or customer-hosted repositories were affected right now.
TeamPCP was linked to big attacks on developer code platforms like GitHub, PyPI, NPM, and Docker. Recently, they were also connected to the “Mini Shai-Hulud” supply chain campaign, which affected two OpenAI employees.
Threat actors are more and more focused on developer tools, IDE add-ons, CI/CD plugins, and package managers to get a way into valuable tech companies.
GitHub’s cloud platform is used by more than 4 million groups (including 90% of the Fortune 100) and over 180 million developers who work on more than 420 million code projects.



